Regarding tracking codes on sales pages?

Hi guys,
i'm trying to launch a product on warriorplus. i embed a tracking code for affiliates who make a sale to earn commissions and for some reason warriorplus cant detect the code. this is what they sent me.
Here is the sales page if needed. https://www.fasteyemarketing.com/the-affiliate-unfair-advantage-fe
Hi there. Thank you for submitting your offer through WarriorPlus. WarriorPlus is currently unable to detect the required tracking codes on your sales page. This is generally caused by an issue with the sales page or hosting configuration, such as: Cloudflare, firewall or bot protection blocking the WarriorPlus verification request Security plugins or server rules restricting access. The tracking code being loaded dynamically rather than being present in the page source Redirects preventing the correct page from being scanned. Caching/CDN serving an older version of the page. The tracking code being incorrectly installed or modified. Please check these settings with your hosting provider/web developer and ensure the WarriorPlus tracking code can be accessed and read by external verification requests. Unfortunately, this is something that will need to be resolved on your side before we can successfully verify the page. If you use the "!" button next to each product, these should be "green" across the board. You'll notice that these are either amber or red meaning there are issues. Thanks. WarriorPlus Approvals Team
Thanks
Edgar Irizarry
-

Hello Edgar,
I can see the WarriorPlus "Add To Cart" button on your sales page: https://www.fasteyemarketing.com/the-affiliate-unfair-advantage-fe.
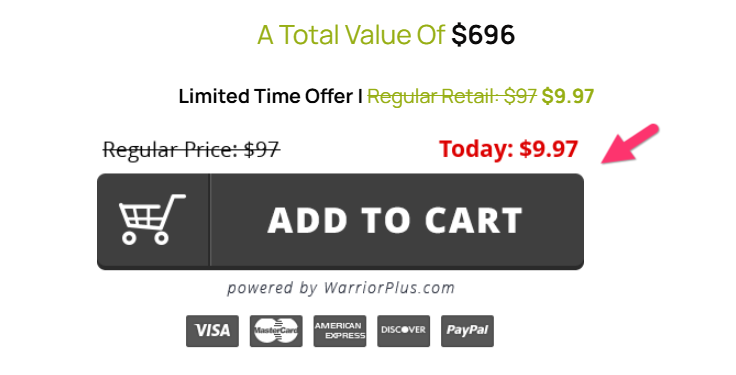
The button clearly displays “Powered by WarriorPlus.com,” and clicking it redirects visitors to the WarriorPlus checkout page: https://warriorplus.com/o2/buy/skhv6c/mf5vd9/l4py4d
Hence I’m not sure what WarriorPlus means by the message: “WarriorPlus is currently unable to detect the required tracking codes on your sales page.”. Could you please clarify which specific tracking codes they’re referring to and where they expect these codes to be installed? This information will help determine whether any additional configuration is needed on your Brizy sales page.
0 -
Thank you for checking the sales page and confirming that the WarriorPlus checkout button works correctly.
WarriorPlus requires a separate sales-page script in addition to the checkout button. Their instructions state:
“REQUIRED: Sales Page Code — Install once before
</body>. Enables sales page features like buttons, tracking, disclaimer and more.”The required script for this offer is:
<script type="text/javascript" src="https://warriorplus.com/o2/js/mf5vd9" defer></script>I reviewed the raw source of the published sales page and confirmed that this script is present once inside the page body and before the closing
</body>tag. I have also moved the Brizy Embed element containing the script near the top of the page and republished it.The issue is that WarriorPlus’s automated verification system still reports that it cannot detect the required tracking code. The functioning checkout button confirms that visitors can reach WarriorPlus, but it does not confirm that the WarriorPlus verification crawler can detect or access the separate tracking script.
Could you please help determine:
-
Whether Brizy’s CDN, firewall, bot protection, or caching could serve different page content to an external verification crawler.
-
Whether scripts placed inside a Brizy Embed element can be detected in the raw HTML by automated crawlers.
-
Whether Brizy modifies the script in a way that could affect detection. In the published source,
deferappears asdefer="". -
Whether there is a page-specific method for inserting this script directly before
</body>without adding it globally to every page on the Fast Eye Marketing website.
The script is product-specific, so using the global website Code Injection setting would place it on unrelated pages.
WarriorPlus has advised that the issue may result from Cloudflare, firewall or bot protection, dynamically loaded code, redirects, caching/CDN behavior, or modified installation.
Thank you for helping me determine whether any Brizy configuration is preventing the WarriorPlus verification crawler from recognizing the script.
Best regards,
Edgar Irizarry
Fast Eye Marketing0 -
-
Hello Edgar,
Brizy Cloud uses a Cloud Web Application Firewall (WAF) as a key layer of protection for our infrastructure. The WAF monitors and filters incoming traffic before it reaches our web servers, helping protect websites and maintain the security and reliability of the platform.
Its protection covers several important areas:
- Protection against common web exploits: Automatically blocks common attacks such as SQL injection, cross-site scripting (XSS), and remote code execution (RCE).
- Protection against malicious bots and automated attacks: Uses bot controls and rate limiting to help mitigate threats such as account takeover attempts, content scraping, and certain types of denial-of-service (DDoS) attacks.
- Scalable protection for custom domains: Inspects incoming requests across customer websites using custom domains and dynamically generated subdomains, helping protect the platform at scale while maintaining performance.
- Centralized security and traffic control: Enables our platform engineers to apply global security rules across the infrastructure and dynamically manage protections through AWS WAF APIs.
- Security monitoring and logging: Provides visibility into incoming traffic and access logs, helping with security investigations and the monitoring of website activity, including traffic to e-commerce sites and lead-generation pages.
Given these security measures, it’s possible that our WAF blocked the WarriorPlus verification crawler, although we would need to investigate the relevant logs to confirm this.
Could you please clarify whether crawler verification is a mandatory requirement when setting up an affiliate product in WarriorPlus, or whether it is an optional, recommended step? Understanding this will help us determine the appropriate next steps and assess whether any adjustments to our security rules may be necessary.
0 -
Thank you for explaining Brizy Cloud’s WAF protection. Based on the response I received from WarriorPlus, crawler verification is mandatory for my offer to be approved for the WarriorPlus marketplace.
The offer can technically remain active and private, and sales can be processed. However, WarriorPlus has informed me that the required page checks must display green before they can approve the offer for the marketplace.
Their automated verification currently reports:
“Unable to verify the sales page:
https://www.fasteyemarketing.com/the-affiliate-unfair-advantage-fe
Please make sure the page can be reached and try again.”The required WarriorPlus script is present once in the published page source:
<script type="text/javascript" src="https://warriorplus.com/o2/js/mf5vd9" defer></script>The page is publicly accessible in standard browsers, indexed by Google, and the WarriorPlus checkout button works. This makes the possibility of the Brizy Cloud WAF blocking the WarriorPlus verification crawler particularly relevant.
Could your technical team please review the WAF and access logs for requests to this page from the WarriorPlus verifier?
I most recently ran the verification check on October 23, 2026. If possible, please check for blocked, challenged, rate-limited, or otherwise unsuccessful automated requests to:
https://www.fasteyemarketing.com/the-affiliate-unfair-advantage-fe
If you need a more precise timestamp, IP address, user agent, or other identifying information for the WarriorPlus crawler, I can request that information from WarriorPlus support.
Because I plan to use Brizy Cloud for additional WarriorPlus sales funnels, resolving this compatibility issue is important for my current offer and future product launches.
Thank you for investigating this further.
Edgar Irizarry
Fast Eye Marketing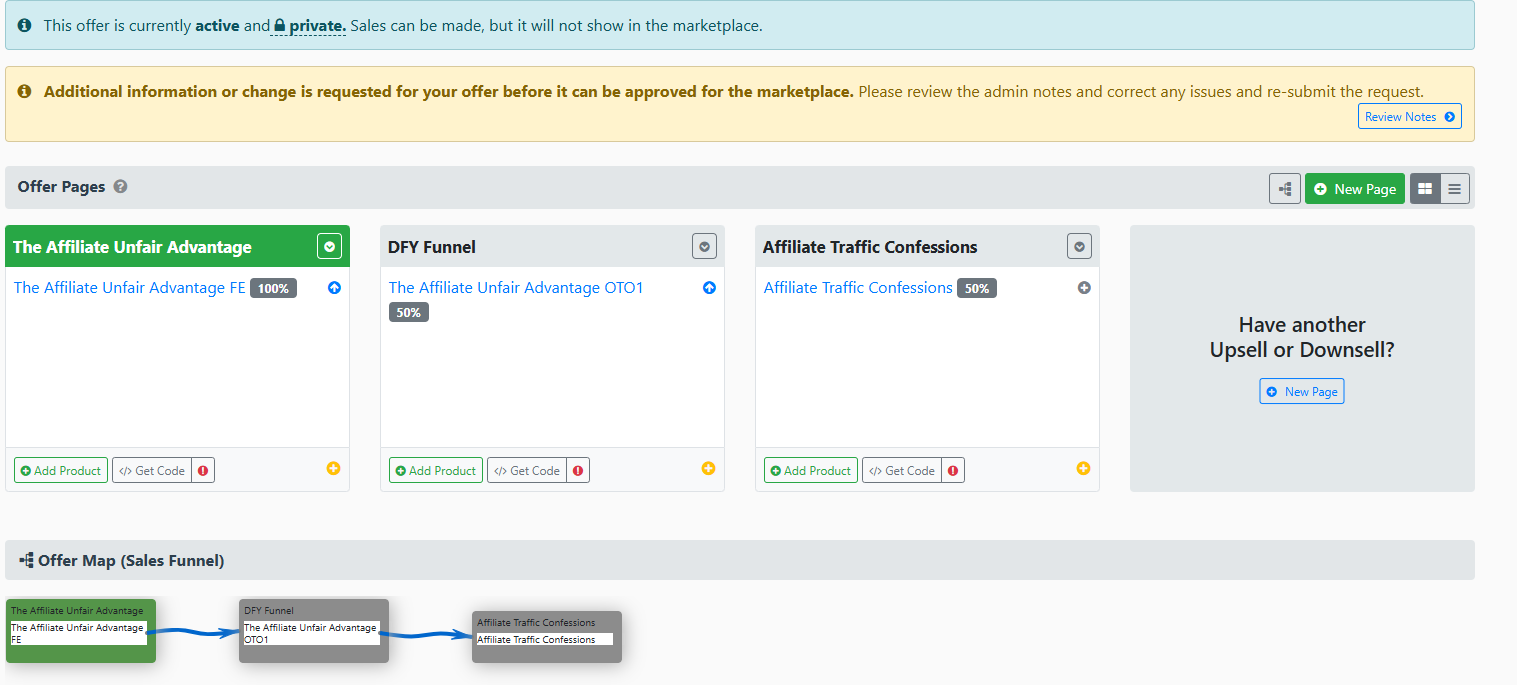 0
-
Hello Edgar,
First, please accept our apologies for the delayed response. Our support team is closed on weekends, and we appreciate your patience.
We’re open to reviewing and, where appropriate, adjusting our Web Application Firewall (WAF) security rules to allow legitimate WarriorPlus verification requests while maintaining the security of the Brizy Cloud infrastructure.
To help us identify whether our WAF is blocking these requests and determine the safest way to resolve the issue, could you please share the following details?
- Target URL: Could you confirm whether the URL being verified is https://www.fasteyemarketing.com/the-affiliate-unfair-advantage-fe?
- User-Agent string: Does WarriorPlus use a specific User-Agent header for its verification crawler? If so, please share the exact value.
- Request method: Is the verification performed through an HTTP POST request, such as an IPN (Instant Payment Notification) webhook, or does it use a different method?
- WarriorPlus IP addresses: Could you provide the official IP addresses or IP ranges used by WarriorPlus for verification requests and IPN callbacks?
- Exact timestamp of a failed attempt: If you have access to the relevant logs, please share the date, time, and timezone of a failed verification attempt. This will help us locate the corresponding request in our WAF logs and identify which security rule, if any, blocked it.
If you’re unable to obtain all these details, that’s fine. Please share whatever information you have, and we’ll use it to guide our investigation.
Thank you for your cooperation. With these details, we can better pinpoint the cause and assess the appropriate adjustments to help WarriorPlus verification work reliably without compromising the security of Brizy Cloud.
0
Please sign in to leave a comment.
Comments
5 comments